California
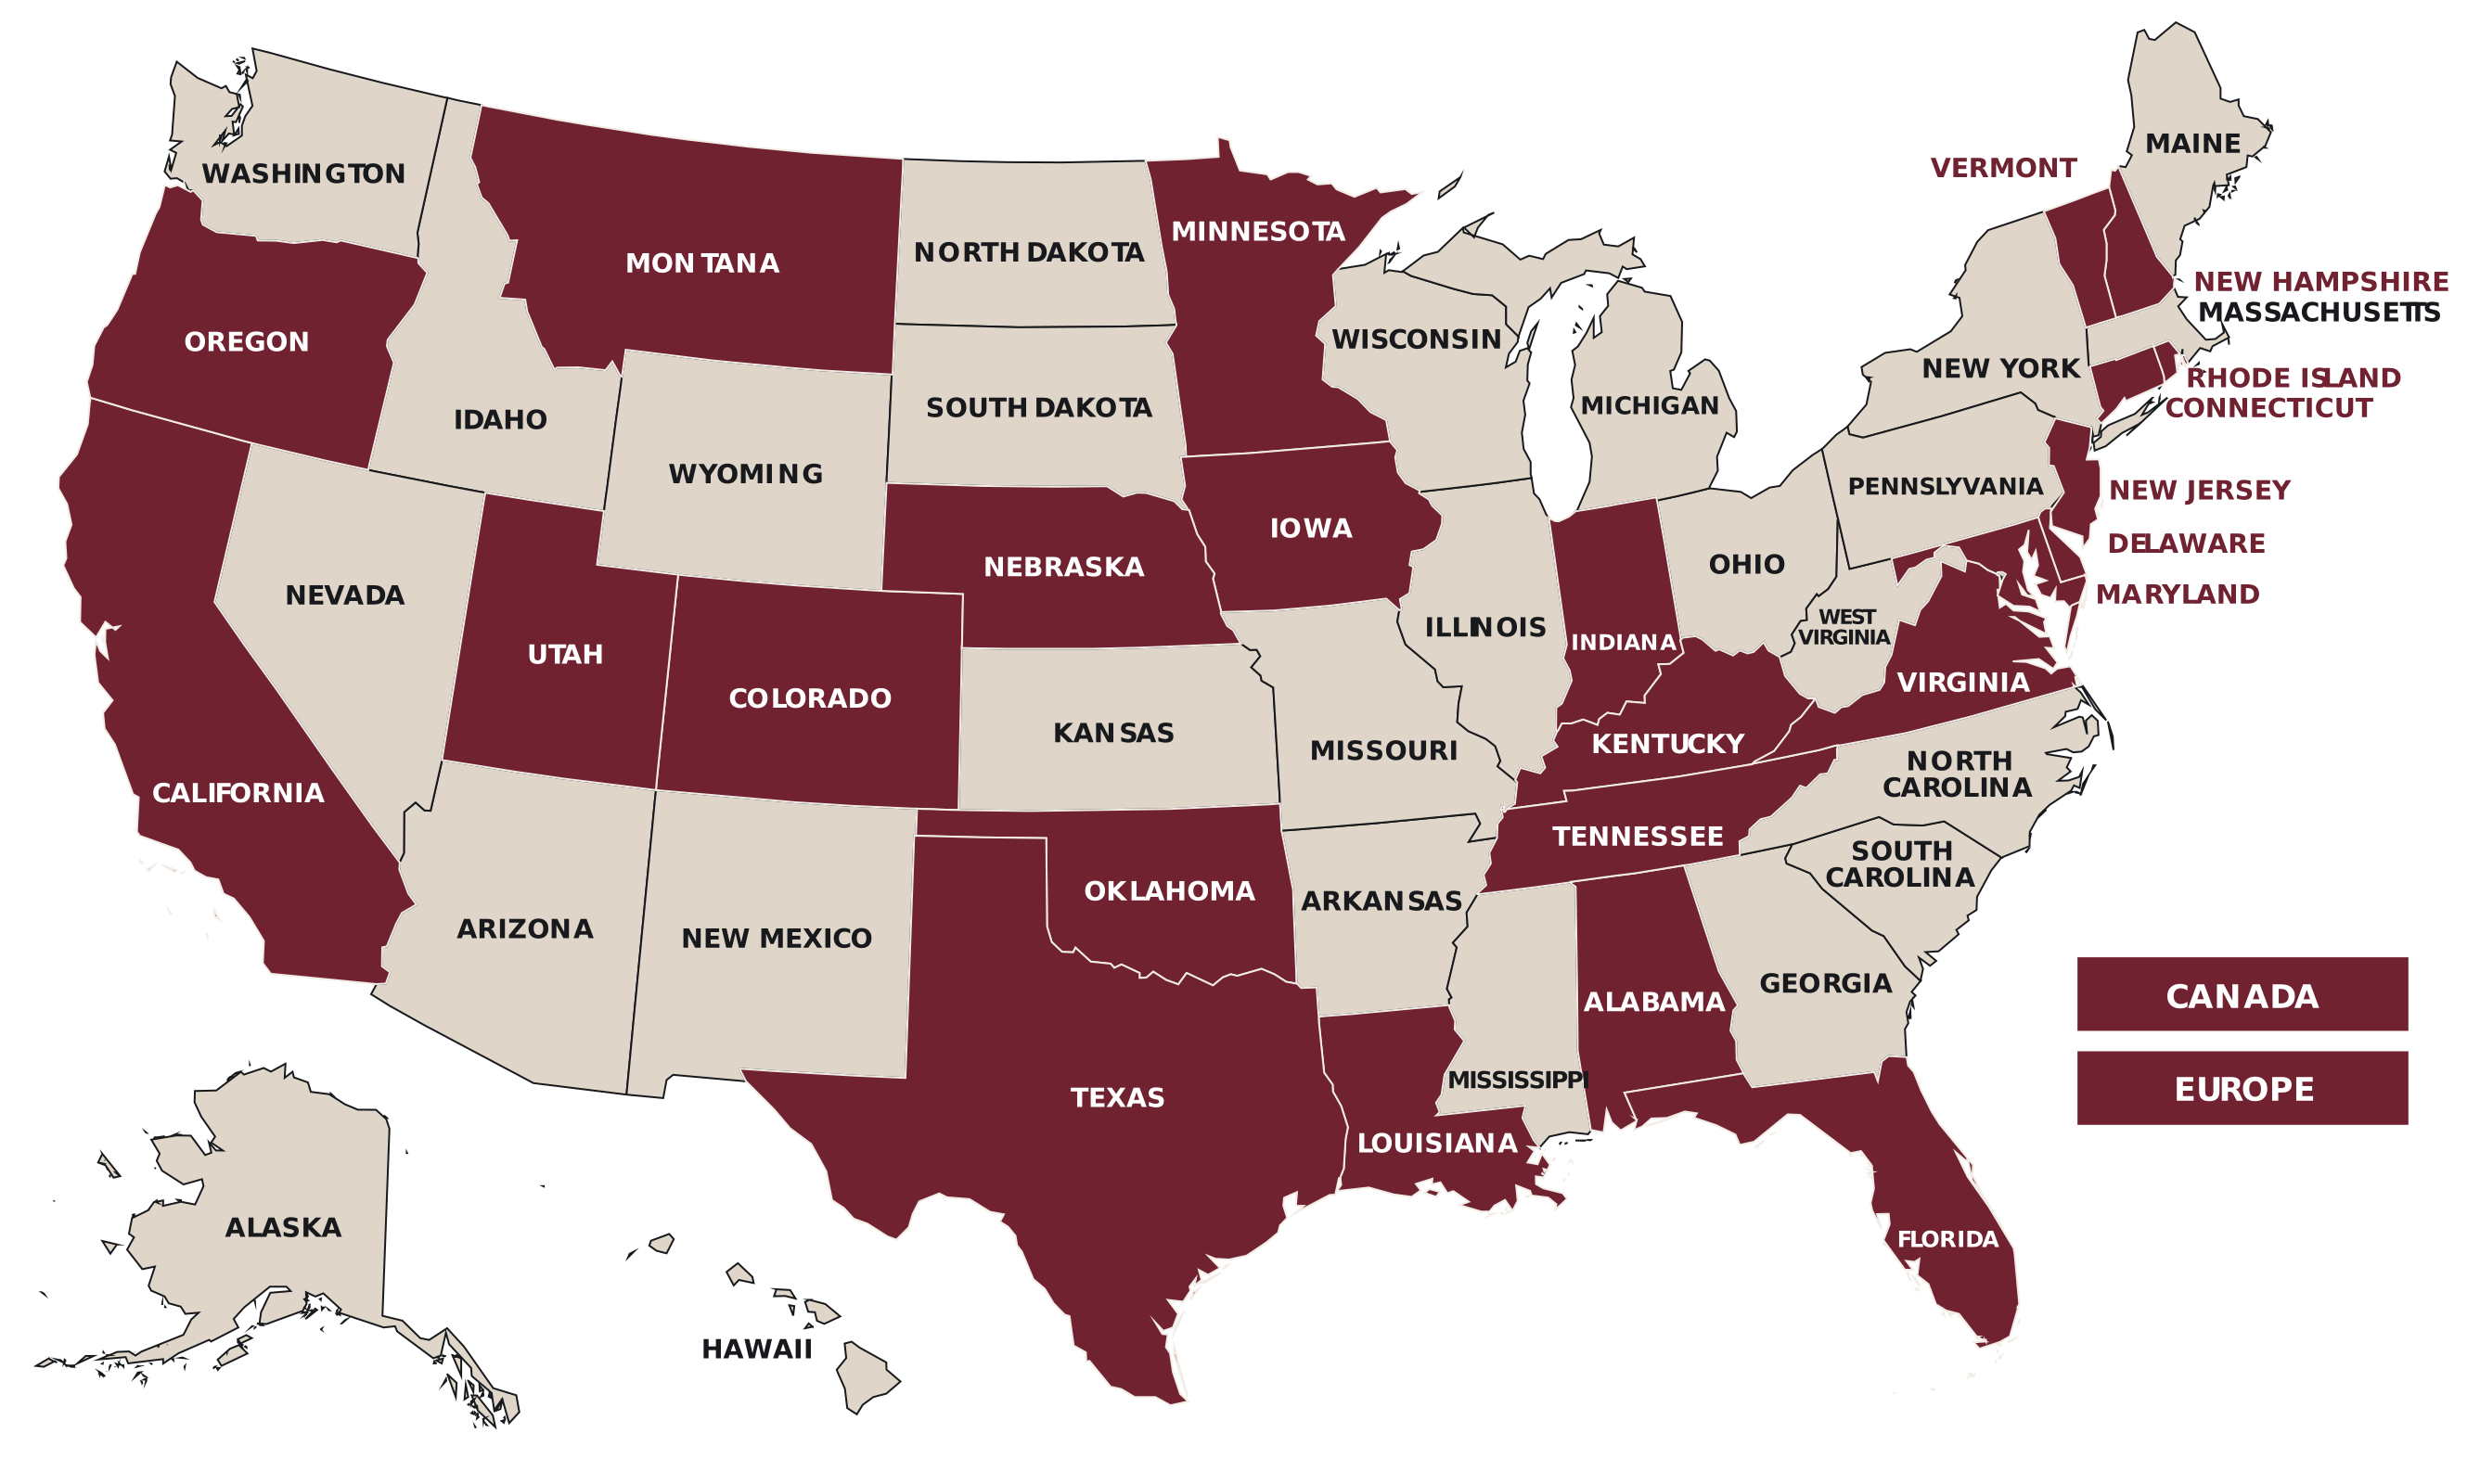
The California Consumer Privacy Act (CCPA), as amended by the California Privacy Rights Act (CPRA), gives California residents rights concerning how covered businesses collect, use, share, and sell their personal information. These rights include access, correction, deletion, and data portability, as well as the ability to opt out of the sale or sharing of personal information and limit certain uses of sensitive personal information.
The law generally applies to for-profit businesses doing business in California that meet at least one statutory threshold, including the inflation-adjusted annual gross revenue threshold, processing the personal information of 100,000 or more consumers or households, or deriving at least 50% of annual revenue from selling or sharing consumers' personal information. Covered businesses must provide appropriate privacy notices and mechanisms for consumers to exercise their rights.
Request a ConsultationColorado
The Colorado Privacy Act (CPA), effective July 1, 2023, provides Colorado residents with rights to access, correct, delete, and obtain portable copies of their personal data. Consumers may also opt out of targeted advertising, the sale of personal data, and certain profiling used to make decisions with legal or similarly significant effects.
The CPA generally applies to entities conducting business in Colorado or producing products or services intentionally targeted to Colorado residents that meet applicable data-processing thresholds. Covered organizations must provide privacy notices, obtain consent for certain sensitive-data processing, maintain appropriate safeguards, and conduct data protection assessments for specified higher-risk processing activities.
Request a ConsultationConnecticut
The Connecticut Data Privacy Act (CTDPA), originally effective July 1, 2023, gives Connecticut residents rights to access, correct, delete, and obtain copies of personal data. Consumers can also opt out of targeted advertising, the sale of personal data, and certain profiling. Connecticut has subsequently expanded the law's scope and protections.
Beginning July 1, 2026, expanded coverage generally includes entities that process the personal data of at least 35,000 consumers, process certain sensitive data, or offer consumers' personal data for sale, subject to statutory exemptions and qualifications. Covered organizations must comply with privacy-notice, consent, data-security, consumer-rights, and data-protection-assessment requirements.
Request a ConsultationDelaware
The Delaware Personal Data Privacy Act (DPDPA), effective January 1, 2025, provides Delaware residents with rights to access, correct, delete, and obtain copies of their personal data. Consumers can also opt out of targeted advertising, certain profiling, and the sale of personal data.
The DPDPA generally applies to entities controlling or processing the personal data of at least 35,000 consumers, or at least 10,000 consumers when more than 20% of gross revenue is derived from the sale of personal data. Covered organizations must provide privacy notices, implement reasonable security practices, and conduct data protection assessments for certain processing activities.
Request a ConsultationFlorida
Florida's Digital Bill of Rights, effective July 1, 2024, establishes privacy rights for consumers whose personal data is processed by covered businesses. These include rights to access, correct, delete, and obtain copies of personal data, along with rights to opt out of targeted advertising, the sale of personal data, and certain profiling.
The law applies more narrowly than many other state comprehensive privacy laws and primarily targets certain large technology and digital businesses meeting statutory revenue and business-model requirements. Covered controllers have obligations involving privacy notices, consumer requests, sensitive data, data security, and specified data-processing practices.
Request a ConsultationIndiana
The Indiana Consumer Data Protection Act (ICDPA), effective January 1, 2026, provides Indiana consumers with rights to access, correct, delete, and obtain portable copies of personal data. Consumers can also opt out of targeted advertising, the sale of personal data, and certain profiling.
The ICDPA generally applies to entities conducting business in Indiana or targeting Indiana residents that process the personal data of at least 100,000 consumers, or at least 25,000 consumers while deriving more than 50% of gross revenue from personal-data sales. Covered controllers must provide privacy notices, protect personal data, obtain consent before processing sensitive data, and conduct data protection assessments for specified activities.
Request a ConsultationIowa
The Iowa Consumer Data Protection Act, effective January 1, 2025, provides Iowa consumers with rights to access and delete certain personal data and obtain portable copies of data they previously provided. Consumers may also opt out of the sale of their personal data.
The law generally applies to entities controlling or processing personal data of at least 100,000 Iowa consumers, or at least 25,000 consumers when more than 50% of gross revenue is derived from personal-data sales. Covered organizations must provide privacy notices, maintain reasonable safeguards, and comply with requirements governing sensitive data and consumer requests.
Request a ConsultationKentucky
The Kentucky Consumer Data Protection Act (KCDPA), effective January 1, 2026, gives Kentucky consumers rights to access, correct, delete, and obtain portable copies of their personal data. Consumers may also opt out of targeted advertising, the sale of personal data, and profiling used to make decisions that produce legal or similarly significant effects.
The KCDPA generally applies to controllers processing personal data of at least 100,000 Kentucky consumers, or at least 25,000 consumers when 50% or more of gross revenue is derived from the sale of personal data. Covered controllers must provide clear privacy notices, obtain consent before processing sensitive data, maintain appropriate data-security practices, and comply with consumer requests.
Request a ConsultationMaryland
The Maryland Online Data Privacy Act (MODPA), effective October 1, 2025, gives Maryland consumers rights to access, correct, delete, and obtain copies of personal data. Consumers may also opt out of targeted advertising, the sale of personal data, and certain profiling.
MODPA generally applies to entities controlling or processing the personal data of at least 35,000 consumers, or at least 10,000 consumers when more than 20% of gross revenue is derived from personal-data sales. The law also establishes significant data-minimization requirements and restrictions concerning sensitive data and certain processing involving minors.
Request a ConsultationMinnesota
The Minnesota Consumer Data Privacy Act (MCDPA), effective July 31, 2025, gives Minnesota residents rights to access, correct, delete, and obtain copies of their personal data. Consumers can opt out of targeted advertising, data sales, and certain profiling and may obtain information concerning third parties to whom their data has been sold.
The MCDPA generally applies to businesses processing personal data of at least 100,000 Minnesota consumers, or at least 25,000 consumers when more than 25% of gross revenue is derived from personal-data sales. Covered businesses must minimize data collection, maintain appropriate security practices, provide privacy notices, obtain consent for sensitive-data processing, and conduct required data assessments.
Request a ConsultationMontana
The Montana Consumer Data Privacy Act (MCDPA) gives Montana consumers rights to access, correct, delete, and obtain portable copies of personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
Following amendments to the law, coverage generally includes controllers processing personal data of at least 25,000 Montana consumers, or at least 15,000 consumers when more than 25% of gross revenue is derived from personal-data sales. Covered controllers must provide appropriate privacy notices, protect consumer data, obtain consent for certain sensitive-data processing, and conduct data protection assessments.
Request a ConsultationNebraska
The Nebraska Data Privacy Act provides Nebraska consumers with rights to access, correct, delete, and obtain portable copies of their personal data. Consumers may also opt out of targeted advertising, the sale of personal data, and certain profiling.
Unlike many state privacy laws, Nebraska does not rely primarily on fixed consumer-volume thresholds. The law generally applies to businesses operating in Nebraska or producing products or services consumed by Nebraska residents that process or sell personal data and are not considered small businesses under the federal Small Business Act, subject to statutory exemptions. Small businesses remain subject to certain requirements concerning the sale of sensitive data.
Request a ConsultationNew Hampshire
The New Hampshire Data Privacy Act, effective January 1, 2025, provides residents with rights to access, correct, delete, and obtain portable copies of personal data. Consumers may also opt out of targeted advertising, the sale of personal data, and certain profiling.
The law generally applies to entities processing personal data of at least 35,000 consumers, or at least 10,000 consumers when more than 25% of gross revenue is derived from personal-data sales. Covered organizations must provide privacy notices, obtain consent before processing sensitive data, maintain reasonable security practices, and conduct data protection assessments for specified processing activities.
Request a ConsultationNew Jersey
The New Jersey Data Privacy Act, effective January 15, 2025, gives New Jersey consumers rights to access, correct, delete, and obtain copies of their personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
The law generally applies to controllers processing personal data of at least 100,000 consumers, or at least 25,000 consumers when the controller derives revenue or receives discounts from the sale of personal data. Covered organizations must provide privacy notices, protect personal data, obtain consent for sensitive-data processing, and conduct data protection assessments for specified higher-risk activities.
Request a ConsultationOregon
The Oregon Consumer Privacy Act (OCPA), effective for most covered entities July 1, 2024, gives Oregon consumers rights to access, correct, delete, and obtain copies of personal data. Consumers may also opt out of targeted advertising, personal-data sales, and certain profiling.
The OCPA generally applies to organizations processing personal data of at least 100,000 consumers, or at least 25,000 consumers while deriving 25% or more of annual gross revenue from personal-data sales. Most qualifying nonprofit organizations became subject to the law on July 1, 2025. Covered organizations must provide privacy notices, obtain consent for sensitive-data processing, and conduct data protection assessments for specified activities.
Request a ConsultationRhode Island
The Rhode Island Data Transparency and Privacy Protection Act, effective January 1, 2026, provides Rhode Island consumers with rights concerning access, correction, deletion, and portability of personal data. Consumers may also opt out of targeted advertising, the sale of personal data, and certain profiling.
The law generally applies to entities processing personal data of at least 35,000 Rhode Island consumers, or at least 10,000 consumers when more than 20% of gross revenue is derived from personal-data sales. Covered organizations must provide required privacy disclosures and comply with requirements concerning consumer requests, sensitive data, security, and specified data-processing activities.
Request a ConsultationTennessee
The Tennessee Information Protection Act (TIPA), effective July 1, 2025, provides Tennessee consumers with rights to access, correct, delete, and obtain portable copies of personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
TIPA generally applies to businesses processing personal data of at least 100,000 consumers, or at least 25,000 consumers when more than 50% of gross revenue is derived from personal-data sales. Covered controllers must provide privacy notices, protect personal information, obtain consent before processing sensitive data, and conduct data protection assessments for specified processing activities.
Request a ConsultationTexas
The Texas Data Privacy and Security Act (TDPSA), effective July 1, 2024, gives Texas consumers rights to access, correct, delete, and obtain portable copies of personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
The TDPSA does not use the consumer-volume thresholds found in many other state privacy laws. It generally applies to entities conducting business in Texas or producing products or services consumed by Texas residents that process or sell personal data and are not small businesses as defined by the U.S. Small Business Administration, subject to statutory exemptions. Small businesses remain subject to restrictions involving the sale of sensitive data.
Request a ConsultationUtah
The Utah Consumer Privacy Act (UCPA), effective December 31, 2023, gives Utah consumers rights to access and delete certain personal data and obtain portable copies of data they previously provided. Consumers can also opt out of targeted advertising and the sale of personal data.
The UCPA generally applies to qualifying entities with annual revenue of at least $25 million that also meet statutory data-processing or personal-data-sale thresholds. Covered controllers must provide privacy notices, maintain reasonable security practices, and obtain consent before processing certain sensitive data involving children.
Request a ConsultationVermont
Vermont enacted the Vermont Data Privacy and Online Surveillance Act in June 2026. The law establishes comprehensive consumer privacy protections governing the collection, use, sale, and other processing of personal data, including additional protections concerning sensitive information and online surveillance.
The law covers qualifying organizations that process personal data of at least 35,000 consumers, process sensitive data of at least 3,000 consumers, or sell personal data of at least 3,000 consumers, subject to statutory exemptions. Because the law includes provisions with future effective dates, organizations should review the applicable implementation timeline when determining their obligations.
Request a ConsultationVirginia
The Virginia Consumer Data Protection Act (VCDPA), effective January 1, 2023, gives Virginia consumers rights to access, correct, delete, and obtain portable copies of their personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
The VCDPA generally applies to entities conducting business in Virginia or targeting Virginia residents that process personal data of at least 100,000 consumers, or at least 25,000 consumers while deriving more than 50% of gross revenue from personal-data sales. Covered controllers must provide privacy notices, obtain consent before processing sensitive data, implement appropriate security practices, and conduct data protection assessments.
Request a ConsultationAlabama
The Alabama Personal Data Protection Act (APDPA), enacted in 2026 and effective May 1, 2027, gives Alabama consumers rights to access, correct, delete, and obtain portable copies of their personal data. Consumers can also opt out of the sale of personal data, targeted advertising, and certain profiling.
The APDPA generally applies to entities conducting business in Alabama or targeting Alabama residents that control or process personal data of at least 25,000 consumers, or derive more than 25% of gross revenue from the sale of personal data, subject to statutory exemptions. Covered organizations must provide privacy notices, maintain appropriate data-security practices, and comply with consumer requests and requirements governing sensitive data.
Request a ConsultationLouisiana
The Louisiana Data Privacy Act (LDPA), enacted in 2026 and effective January 1, 2027, gives Louisiana consumers rights to access, correct, delete, and obtain portable copies of their personal data. Consumers can also opt out of targeted advertising, the sale of personal data, and certain profiling.
The LDPA generally applies to entities doing business in Louisiana that meet at least one statutory threshold, including annual gross revenue exceeding $25 million, processing the personal data of at least 75,000 consumers, households, or devices, or deriving at least 50% of annual revenue from the sale of personal data. Covered organizations must provide privacy notices, protect personal data, comply with consumer requests, and conduct data protection assessments for specified processing activities.
Request a ConsultationOklahoma
The Oklahoma Consumer Data Privacy Act, enacted in 2026 and effective January 1, 2027, gives Oklahoma consumers rights to access, correct, delete, and obtain portable copies of their personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
The law generally applies to entities conducting business in Oklahoma or targeting Oklahoma residents that process personal data of at least 100,000 consumers, or at least 25,000 consumers while deriving more than 50% of gross revenue from personal-data sales. Covered controllers must provide privacy notices, protect personal data, obtain consent before processing sensitive data, and conduct data protection assessments for specified higher-risk processing activities.
Request a ConsultationCanada
The Personal Information Protection and Electronic Documents Act (PIPEDA) is Canada's federal private-sector privacy law. It establishes principles governing the collection, use, disclosure, accuracy, safeguarding, retention, and accessibility of personal information in commercial activities.
PIPEDA generally applies to private-sector organizations engaged in commercial activities where federal privacy requirements apply, including certain interprovincial and international transfers of personal information. Organizations subject to PIPEDA must report qualifying breaches that create a real risk of significant harm, notify affected individuals, and maintain records of security breaches as required by law.
Request a ConsultationEurope
The General Data Protection Regulation (GDPR), applicable since May 25, 2018, establishes privacy and data-protection requirements across the European Union and European Economic Area. It provides individuals with rights involving access, rectification, erasure, restriction, portability, objection, and certain automated decision-making.
The GDPR applies to organizations established in the EU and can also apply to organizations outside the EU when they offer goods or services to people in the EU or monitor their behavior there. Controllers must implement appropriate technical and organizational safeguards and, when a qualifying personal-data breach occurs, generally notify the appropriate supervisory authority within 72 hours after becoming aware of it.
Request a ConsultationNorth America
Alabama
Alabama
The Alabama Personal Data Protection Act (APDPA), enacted in 2026 and effective May 1, 2027, gives Alabama consumers rights to access, correct, delete, and obtain portable copies of their personal data. Consumers can also opt out of targeted advertising, the sale of personal data, and certain profiling.
The APDPA generally applies to entities conducting business in Alabama or targeting Alabama residents that control or process personal data of at least 25,000 consumers, or derive more than 25% of gross revenue from the sale of personal data, subject to statutory exemptions. Covered organizations must provide privacy notices, maintain appropriate data-security practices, and comply with consumer requests and requirements governing sensitive data.
California
California
The California Consumer Privacy Act (CCPA), as amended by the California Privacy Rights Act (CPRA), gives California residents rights concerning how covered businesses collect, use, share, and sell their personal information. These rights include access, correction, deletion, and data portability, as well as the ability to opt out of the sale or sharing of personal information and limit certain uses of sensitive personal information.
The law generally applies to for-profit businesses doing business in California that meet at least one statutory threshold, including the inflation-adjusted annual gross revenue threshold, processing the personal information of 100,000 or more consumers or households, or deriving at least 50% of annual revenue from selling or sharing consumers' personal information. Covered businesses must provide appropriate privacy notices and mechanisms for consumers to exercise their rights.
Canada
Canada
The Personal Information Protection and Electronic Documents Act (PIPEDA) is Canada's federal private-sector privacy law. It establishes principles governing the collection, use, disclosure, accuracy, safeguarding, retention, and accessibility of personal information in commercial activities.
PIPEDA generally applies to private-sector organizations engaged in commercial activities where federal privacy requirements apply, including certain interprovincial and international transfers of personal information. Organizations subject to PIPEDA must report qualifying breaches that create a real risk of significant harm, notify affected individuals, and maintain records of security breaches as required by law.
Colorado
Colorado
The Colorado Privacy Act (CPA), effective July 1, 2023, provides Colorado residents with rights to access, correct, delete, and obtain portable copies of their personal data. Consumers may also opt out of targeted advertising, the sale of personal data, and certain profiling used to make decisions with legal or similarly significant effects.
The CPA generally applies to entities conducting business in Colorado or producing products or services intentionally targeted to Colorado residents that meet applicable data-processing thresholds. Covered organizations must provide privacy notices, obtain consent for certain sensitive-data processing, maintain appropriate safeguards, and conduct data protection assessments for specified higher-risk processing activities.
Connecticut
Connecticut
The Connecticut Data Privacy Act (CTDPA), originally effective July 1, 2023, gives Connecticut residents rights to access, correct, delete, and obtain copies of personal data. Consumers can also opt out of targeted advertising, the sale of personal data, and certain profiling. Connecticut has subsequently expanded the law's scope and protections.
Beginning July 1, 2026, expanded coverage generally includes entities that process the personal data of at least 35,000 consumers, process certain sensitive data, or offer consumers' personal data for sale, subject to statutory exemptions and qualifications. Covered organizations must comply with privacy-notice, consent, data-security, consumer-rights, and data-protection-assessment requirements.
Delaware
Delaware
The Delaware Personal Data Privacy Act (DPDPA), effective January 1, 2025, provides Delaware residents with rights to access, correct, delete, and obtain copies of their personal data. Consumers can also opt out of targeted advertising, certain profiling, and the sale of personal data.
The DPDPA generally applies to entities controlling or processing the personal data of at least 35,000 consumers, or at least 10,000 consumers when more than 20% of gross revenue is derived from the sale of personal data. Covered organizations must provide privacy notices, implement reasonable security practices, and conduct data protection assessments for certain processing activities.
Florida
Florida
Florida's Digital Bill of Rights, effective July 1, 2024, gives consumers covered by the law rights to access, correct, delete, and obtain copies of their personal data. Consumers can also opt out of targeted advertising, the sale of personal data, and certain profiling.
The law applies more narrowly than many other state comprehensive privacy laws and primarily covers certain large technology and digital businesses that meet statutory revenue and business-model requirements. Covered controllers must comply with requirements involving privacy notices, consumer requests, sensitive data, data security, and specified data-processing practices.
Indiana
Indiana
The Indiana Consumer Data Protection Act (ICDPA), effective January 1, 2026, provides Indiana consumers with rights to access, correct, delete, and obtain portable copies of personal data. Consumers can also opt out of targeted advertising, the sale of personal data, and certain profiling.
The ICDPA generally applies to entities conducting business in Indiana or targeting Indiana residents that process the personal data of at least 100,000 consumers, or at least 25,000 consumers while deriving more than 50% of gross revenue from personal-data sales. Covered controllers must provide privacy notices, protect personal data, obtain consent before processing sensitive data, and conduct data protection assessments for specified activities.
Iowa
Iowa
The Iowa Consumer Data Protection Act (ICDPA), effective January 1, 2025, provides Iowa consumers with rights to access and delete certain personal data and obtain portable copies of data they previously provided. Consumers may also opt out of the sale of their personal data.
The law generally applies to entities controlling or processing personal data of at least 100,000 Iowa consumers, or at least 25,000 consumers when more than 50% of gross revenue is derived from personal-data sales. Covered organizations must provide privacy notices, maintain reasonable safeguards, and comply with requirements governing sensitive data and consumer requests.
Kentucky
Kentucky
The Kentucky Consumer Data Protection Act (KCDPA), effective January 1, 2026, gives Kentucky consumers rights to access, correct, delete, and obtain portable copies of their personal data. Consumers may also opt out of targeted advertising, the sale of personal data, and profiling used to make decisions that produce legal or similarly significant effects.
The KCDPA generally applies to controllers processing personal data of at least 100,000 Kentucky consumers, or at least 25,000 consumers when 50% or more of gross revenue is derived from the sale of personal data. Covered controllers must provide clear privacy notices, obtain consent before processing sensitive data, maintain appropriate data-security practices, and comply with consumer requests.
Louisiana
Louisiana
The Louisiana Data Privacy Act (LDPA), enacted in 2026 and effective January 1, 2027, gives Louisiana consumers rights to access, correct, delete, and obtain portable copies of their personal data. Consumers can also opt out of targeted advertising, the sale of personal data, and certain profiling.
The LDPA generally applies to entities doing business in Louisiana that meet at least one statutory threshold, including annual gross revenue exceeding $25 million, processing the personal data of at least 75,000 consumers, households, or devices, or deriving at least 50% of annual revenue from the sale of personal data. Covered organizations must provide privacy notices, protect personal data, comply with consumer requests, and conduct data protection assessments for specified processing activities.
Maryland
Maryland
The Maryland Online Data Privacy Act (MODPA), effective October 1, 2025, gives Maryland consumers rights to access, correct, delete, and obtain copies of personal data. Consumers may also opt out of targeted advertising, the sale of personal data, and certain profiling.
MODPA generally applies to entities controlling or processing the personal data of at least 35,000 consumers, or at least 10,000 consumers when more than 20% of gross revenue is derived from personal-data sales. The law also establishes significant data-minimization requirements and restrictions concerning sensitive data and certain processing involving minors.
Minnesota
Minnesota
The Minnesota Consumer Data Privacy Act (MCDPA), effective July 31, 2025, gives Minnesota residents rights to access, correct, delete, and obtain copies of their personal data. Consumers can opt out of targeted advertising, data sales, and certain profiling and may obtain information concerning third parties to whom their data has been sold.
The MCDPA generally applies to businesses processing personal data of at least 100,000 Minnesota consumers, or at least 25,000 consumers when more than 25% of gross revenue is derived from personal-data sales. Covered businesses must minimize data collection, maintain appropriate security practices, provide privacy notices, obtain consent for sensitive-data processing, and conduct required data assessments.
Montana
Montana
The Montana Consumer Data Privacy Act (MCDPA) gives Montana consumers rights to access, correct, delete, and obtain portable copies of personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
Following amendments to the law, coverage generally includes controllers processing personal data of at least 25,000 Montana consumers, or at least 15,000 consumers when more than 25% of gross revenue is derived from personal-data sales. Covered controllers must provide appropriate privacy notices, protect consumer data, obtain consent for certain sensitive-data processing, and conduct data protection assessments.
Nebraska
Nebraska
The Nebraska Data Privacy Act provides Nebraska consumers with rights to access, correct, delete, and obtain portable copies of their personal data. Consumers may also opt out of targeted advertising, the sale of personal data, and certain profiling.
Unlike many state privacy laws, Nebraska does not rely primarily on fixed consumer-volume thresholds. The law generally applies to businesses operating in Nebraska or producing products or services consumed by Nebraska residents that process or sell personal data and are not considered small businesses under the federal Small Business Act, subject to statutory exemptions. Small businesses remain subject to certain requirements concerning the sale of sensitive data.
New Hampshire
New Hampshire
The New Hampshire Data Privacy Act, effective January 1, 2025, provides residents with rights to access, correct, delete, and obtain portable copies of personal data. Consumers may also opt out of targeted advertising, the sale of personal data, and certain profiling.
The law generally applies to entities processing personal data of at least 35,000 consumers, or at least 10,000 consumers when more than 25% of gross revenue is derived from personal-data sales. Covered organizations must provide privacy notices, obtain consent before processing sensitive data, maintain reasonable security practices, and conduct data protection assessments for specified processing activities.
New Jersey
New Jersey
The New Jersey Data Privacy Act, effective January 15, 2025, gives New Jersey consumers rights to access, correct, delete, and obtain copies of their personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
The law generally applies to controllers processing personal data of at least 100,000 consumers, or at least 25,000 consumers when the controller derives revenue or receives discounts from the sale of personal data. Covered organizations must provide privacy notices, protect personal data, obtain consent for sensitive-data processing, and conduct data protection assessments for specified higher-risk activities.
Oklahoma
Oklahoma
The Oklahoma Consumer Data Privacy Act, enacted in 2026 and effective January 1, 2027, gives Oklahoma consumers rights to access, correct, delete, and obtain portable copies of their personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
The law generally applies to entities conducting business in Oklahoma or targeting Oklahoma residents that process personal data of at least 100,000 consumers, or at least 25,000 consumers while deriving more than 50% of gross revenue from personal-data sales. Covered controllers must provide privacy notices, protect personal data, obtain consent before processing sensitive data, and conduct data protection assessments for specified higher-risk processing activities.
Oregon
Oregon
The Oregon Consumer Privacy Act (OCPA), effective for most covered entities July 1, 2024, gives Oregon consumers rights to access, correct, delete, and obtain copies of personal data. Consumers may also opt out of targeted advertising, personal-data sales, and certain profiling.
The OCPA generally applies to organizations processing personal data of at least 100,000 consumers, or at least 25,000 consumers while deriving 25% or more of annual gross revenue from personal-data sales. Most qualifying nonprofit organizations became subject to the law on July 1, 2025. Covered organizations must provide privacy notices, obtain consent for sensitive-data processing, and conduct data protection assessments for specified activities.
Rhode Island
Rhode Island
The Rhode Island Data Transparency and Privacy Protection Act, effective January 1, 2026, provides Rhode Island consumers with rights concerning access, correction, deletion, and portability of personal data. Consumers may also opt out of targeted advertising, the sale of personal data, and certain profiling.
The law generally applies to entities processing personal data of at least 35,000 Rhode Island consumers, or at least 10,000 consumers when more than 20% of gross revenue is derived from personal-data sales. Covered organizations must provide required privacy disclosures and comply with requirements concerning consumer requests, sensitive data, security, and specified data-processing activities.
Tennessee
Tennessee
The Tennessee Information Protection Act (TIPA), effective July 1, 2025, provides Tennessee consumers with rights to access, correct, delete, and obtain portable copies of personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
TIPA generally applies to businesses processing personal data of at least 100,000 consumers, or at least 25,000 consumers when more than 50% of gross revenue is derived from personal-data sales. Covered controllers must provide privacy notices, protect personal information, obtain consent before processing sensitive data, and conduct data protection assessments for specified processing activities.
Texas
Texas
The Texas Data Privacy and Security Act (TDPSA), effective July 1, 2024, gives Texas consumers rights to access, correct, delete, and obtain portable copies of personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
The TDPSA does not use the consumer-volume thresholds found in many other state privacy laws. It generally applies to entities conducting business in Texas or producing products or services consumed by Texas residents that process or sell personal data and are not small businesses as defined by the U.S. Small Business Administration, subject to statutory exemptions. Small businesses remain subject to restrictions involving the sale of sensitive data.
Utah
Utah
The Utah Consumer Privacy Act (UCPA), effective December 31, 2023, gives Utah consumers rights to access and delete certain personal data and obtain portable copies of data they previously provided. Consumers can also opt out of targeted advertising and the sale of personal data.
The UCPA generally applies to qualifying entities with annual revenue of at least $25 million that also meet statutory data-processing or personal-data-sale thresholds. Covered controllers must provide privacy notices, maintain reasonable security practices, and obtain consent before processing certain sensitive data involving children.
Vermont
Vermont
The Vermont Data Privacy and Online Surveillance Act, enacted in 2026 and generally effective January 1, 2028, gives Vermont consumers rights to access, correct, delete, and obtain portable copies of their personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
The law generally applies to organizations that process personal data of at least 35,000 Vermont consumers, process sensitive data of at least 3,000 consumers, or sell personal data of at least 3,000 consumers, subject to statutory exemptions. Covered organizations must comply with requirements involving privacy notices, data minimization, sensitive data, consumer rights, security practices, and specified high-risk processing activities.
Virginia
Virginia
The Virginia Consumer Data Protection Act (VCDPA), effective January 1, 2023, gives Virginia consumers rights to access, correct, delete, and obtain portable copies of their personal data. Consumers can also opt out of targeted advertising, personal-data sales, and certain profiling.
The VCDPA generally applies to entities conducting business in Virginia or targeting Virginia residents that process personal data of at least 100,000 consumers, or at least 25,000 consumers while deriving more than 50% of gross revenue from personal-data sales. Covered controllers must provide privacy notices, obtain consent before processing sensitive data, implement appropriate security practices, and conduct data protection assessments.
Europe
Europe
The General Data Protection Regulation (GDPR), applicable since May 25, 2018, establishes privacy and data-protection requirements across the European Union and European Economic Area. It provides individuals with rights involving access, rectification, erasure, restriction, portability, objection, and certain automated decision-making.
The GDPR applies to organizations established in the EU and can also apply to organizations outside the EU when they offer goods or services to people in the EU or monitor their behavior there. Controllers must implement appropriate technical and organizational safeguards and, when a qualifying personal-data breach occurs, generally notify the appropriate supervisory authority within 72 hours after becoming aware of it.